Trust & Security

ToolsGroup Puts Customers First — And That Means Safeguarding Customer Data With a Comprehensive, Multi-Layered Security Program in the ToolsGroup Cloud

Your Data, Safe and Secure in the Cloud

In today's data-driven world, security is paramount.

At ToolsGroup, we understand the critical nature of protecting your information.

That's why we've implemented industry-leading security measures that are designed to protect and secure your data in our cloud systems. This comprehensive overview outlines our commitment to data privacy and transparency. We detail our regulatory compliance, certifications, and supporting processes, all designed to safeguard your information with the utmost care.

Software as a Service

Security isn’t just a checkbox for us. It’s an integral part of our solutions and operations, enabling continuous improvements to keep your data safe.

ToolsGroup delivers modern supply chain solutions as Software as a Service (SaaS). We rely on world-class cloud providers and hyperscalers to deliver our infrastructure, ensuring high performance, seamless scalability and robust security. By utilizing the global data center networks of these leading platforms, we bring the solution closer to users around the world — supporting data residency requirements and minimizing latency. This approach enables us to deliver a resilient, secure, and highly responsive service experience that ensures we can always deliver on our promises of safe and dependable solutions in the cloud.

From the ground up, the ToolsGroup cloud solution employs multiple layers of security to protect customer applications and data:

Security is built into every layer of our architecture and processes, not added as an afterthought.

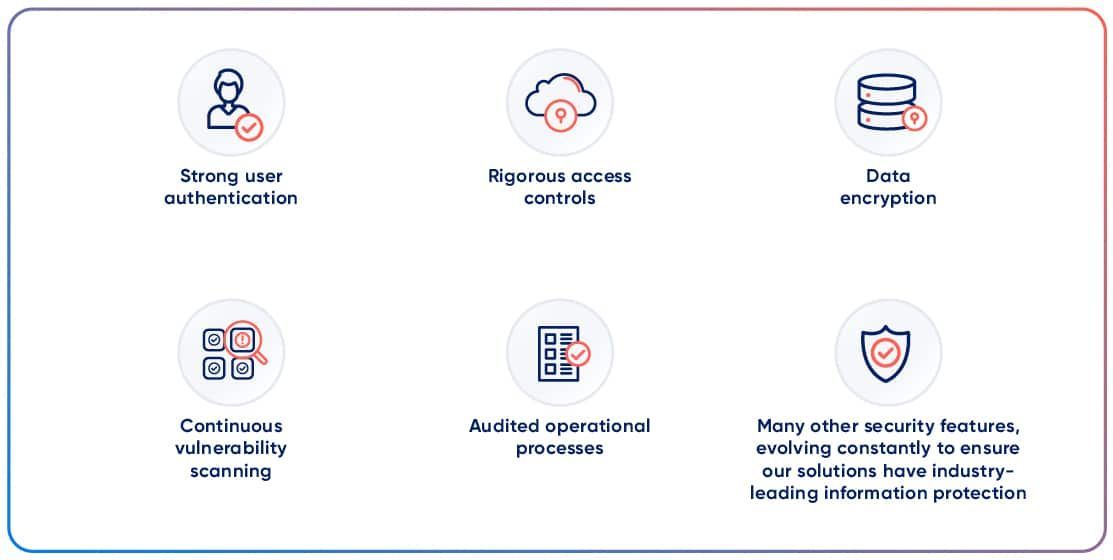
ToolsGroup cloud security layers: strong user authentication, rigorous access controls, data encryption, continuous vulnerability scanning, audited operational processes and many other security features

Data Center and Infrastructure Security

ToolsGroup’s SaaS offering is hosted on Tier 3+ data centers provided by world-class providers. These facilities maintain strict physical security controls to prevent unauthorized access to servers and storage. They use multi-layered security perimeters, biometric and card access systems, 24/7 guarded surveillance, and continuous video monitoring to prevent unauthorized personnel. Regular independent audits and assessments are conducted to ensure the facilities adhere to stringent security requirements and evolving best practices.

Our cloud platform partners are certified against a broad set of industry and government security standards. The underlying infrastructure meets international and regional compliance benchmarks such as ISO/IEC 27001, SOC 1/2/3, and others.

It also adheres to data privacy requirements in various jurisdictions, including EU General Data Protection Regulation (GDPR) and standard contractual clauses for cross-border data transfer. By building on a compliant cloud foundation, ToolsGroup ensures that the physical and environmental security, as well as baseline compliance, are of the highest standard from the start.

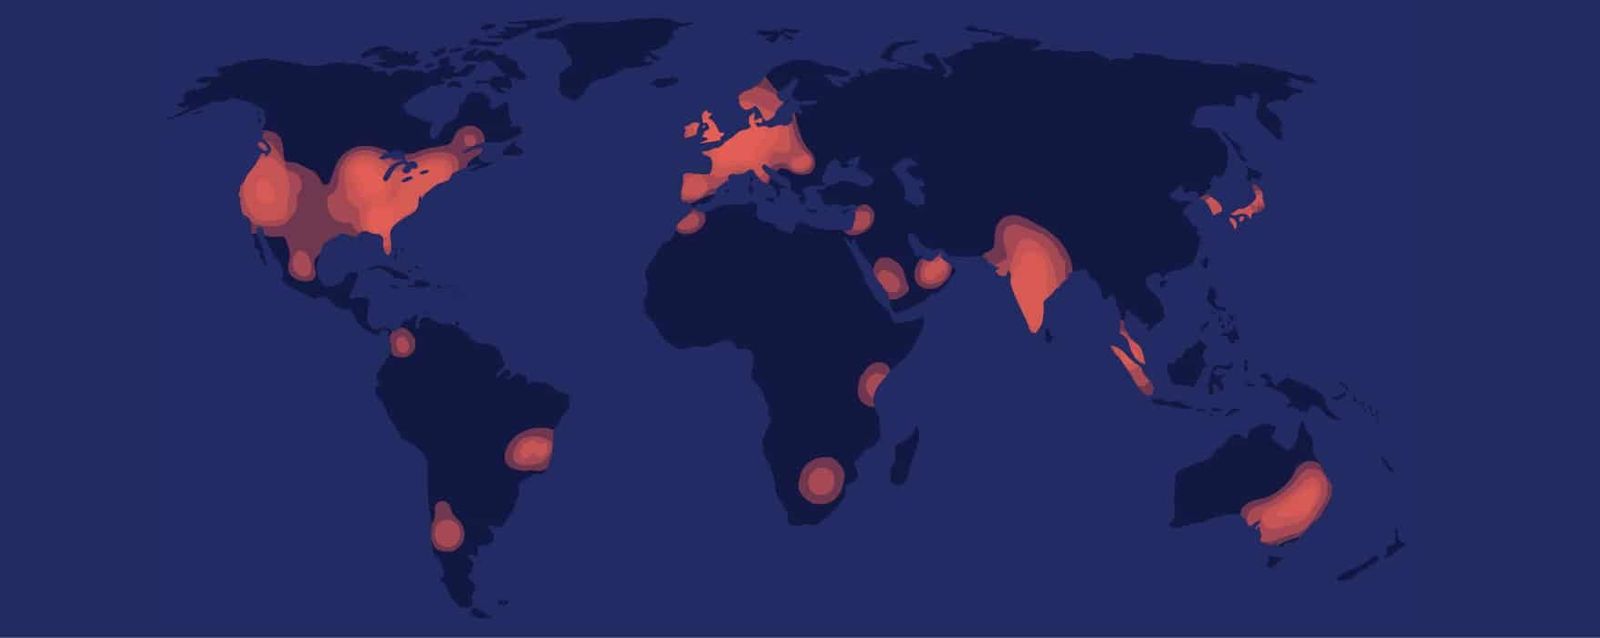
The global presence of our cloud providers’ data centers allows ToolsGroup to deploy your solution in a region that meets your data residency needs and optimizes performance for your users. Our providers operate dozens of regions worldwide, each engineered with redundant power, cooling, and networking, so your data is stored in secure, highly available environments designed to withstand failures and natural disasters. This geographic diversity, combined with careful region selection, helps us comply with local regulations and keep your data close to home. You can see some of the data centers we can use in our heat map.

Heat map of the cloud data center regions ToolsGroup can deploy to

Service Resilience and Data Redundancy

Our cloud architecture inherently provides high availability for critical components, and we back this with a financially guaranteed Service Level Agreement (SLA). ToolsGroup has a documented disaster recovery plan that is tested regularly. In the event of a major outage affecting the primary environment, we can fail over to the secondary region to restore service quickly.

To safeguard availability, ToolsGroup employs robust service redundancy at multiple levels. Any data stored in our solution is kept in redundant copies within the primary hosting region, and it is also asynchronously replicated to a geographically separate secondary region. This geo-redundancy means that even if an entire data center region faces an outage, an up-to-date copy of your data remains available in the backup region, minimizing risk of data loss. The secondary region is carefully chosen to be an appropriate pair for the primary region, balancing distance as well as regulatory requirements.

Data Security and Privacy

Customer Data Ownership

ToolsGroup recognizes that your data is your property. The customer is the exclusive owner of all data put into our solution. We act as a steward of that data, processing and storing it only to fulfill our service obligations.

/ Data At Rest

All data stored on the Solution is encrypted using AES-256, with Keys controlled by ToolsGroup and separate for each Customer.

/ Data In Transit

All data in transit is protected with TLS 1.2 or higher, using modern cipher suites and strong key lengths.

Data Isolation

Each customer’s environment is completely segregated at the application and database level. Your data is stored in its own dedicated database/schema and never co-mingled with anyone else’s data.

Full Encryption, Everywhere

ToolsGroup employs strong encryption to protect customer data in all states: in transit, at rest, and in backups. All data transmitted to and from the application (for example, user traffic between your browser and our cloud) is encrypted in transit using TLS (Transport Layer Security).

Operational Security

Scalability and Performance

ToolsGroup’s cloud solution is designed to scale to meet customer needs without compromising security. We offer standardized deployment tiers (Small, Medium, Large) that cover common workload profiles, and we can further scale resources on demand if your usage grows. This flexible scaling ensures that performance and responsiveness remain optimal as your data volume or user count increases, while keeping the environment secure and stable.

Federated Authentication and Single Sign-On (SSO)

To provide secure and convenient access for users, ToolsGroup supports federated authentication and Single Sign-On (SSO) integration with your identity systems. Federated SSO allows your users to log in to the ToolsGroup application using their existing corporate credentials, managed by your chosen Identity Provider (IdP), such as Azure Active Directory, Okta, PingIdentity, or others.

SSO contributes to stronger security. You can apply uniform login policies, such as requiring MFA or session timeouts, to ToolsGroup via your IdP. This also reduces the risk of weak or reused passwords since users are not creating new credentials for each software. Federated SSO support in ToolsGroup provides enterprise-grade identity management integration, helping you streamline authentication while maintaining full control and visibility.

Security Monitoring and Audit Logging

ToolsGroup maintains centralized logging and real-time monitoring to quickly detect suspicious or abnormal activity across its cloud environment. All key events—such as authentication attempts, user access, and administrative changes—are collected into a Security Information and Event Management (SIEM) system that analyzes patterns and alerts security staff to issues like repeated failed logins, unusual access times, or sudden role changes.

Audit logs are stored in a tamper-resistant repository for at least 180 days to support investigations and compliance needs, with customers able to request relevant records. In addition to security events, an integrated monitoring system tracks system health—covering compute, storage, network, and application performance—and alerts the operations team to issues such as CPU spikes, memory leaks, or slow response times, enabling rapid, proactive response 24/7.

Change Management

ToolsGroup maintains structured procedures on how to manage changes on systems supporting the Solution. All changes are requested and documented through our ticketing portal, assessed for risk and impact (including security), approved by authorized personnel, and scheduled in maintenance windows with advance notice for major updates. Changes are tested and monitored after deployment.
Vulnerability Management and Penetration Testing

ToolsGroup runs a continuous vulnerability management program to identify, assess and remediate security weaknesses across the systems supporting the Solution. Externally exposed systems are scanned for vulnerabilities before go-live and continuously in production, using industry-standard network and application scanning tools.

The SaaS application is also tested by specialized independent third parties. These penetration tests cover the external network and web application and are performed regularly and after significant changes. A summary of the most recent penetration test is available to customers and prospects under NDA.

Findings are prioritized by severity and remediated through our change management process:

  • Critical vulnerabilities are addressed through emergency updates deployed outside regular schedules.
  • High-severity vulnerabilities are prioritized ahead of the regular schedule.
  • Medium- and low-severity vulnerabilities are remediated in regular maintenance windows.

Security updates are tested in non-production environments before staged rollout to production. We also review the cryptographic protocols and cipher suites in use and replace any that no longer meet current security guidelines.

Secure Development

Security is built into how we design, build and release our software. ToolsGroup develops its solutions under a Secure Software Development Lifecycle (SSDLC) that is part of our ISO/IEC 27001:2022-certified Information Security Management System.

  • Peer code review: Every code change is reviewed by experienced developers against secure coding practices before it is merged.
  • Automated security testing: Static code analysis and software composition analysis run in our CI/CD pipelines, and security checks are mandatory on every pull request.
  • Dependency management: Third-party libraries and components are checked regularly for known vulnerabilities and kept up to date.
  • Secrets protection: Credentials and keys are kept out of source code and managed in secure vaults.
  • Environment separation: Development, test and production environments are separated.
  • Developer training: Developers receive ongoing training on secure coding and emerging threats.

ToolsGroup Operators

ToolsGroup Operators working on the systems supporting the Solution connect to customer environments over encrypted channels with MFA for all sensitive operations. ToolsGroup workstations use full-disk encryption and have no direct access to customer data; administration is performed through bastion hosts that separate the corporate network from customer environments.

Disaster Recovery and Business Continuity

ToolsGroup maintains up-to-date plans to manage the most common scenarios that can affect business continuity. These plans are tested yearly or more frequently if required by any significant change to the affected process and audited yearly as part of ToolsGroup’s ISO 27001 certification process.

To support this, and provide resiliency to the Solution, ToolsGroup provides business continuity in the following ways:

  • High availability for the underlying infrastructure and components.
  • Disaster Recovery in a secondary region.
  • Frequent Backups with multiple redundant copies.
  • Comprehensive monitoring to detect anomalies and events relating to outages and other events that may require immediate action. The monitoring system collects data from all systems that compose the Solution and can also issue alerts related to hardware and network capacity as well as security events and attacks.

Data that composes the Solution is organized in three layers:

01 / Virtualization layer

Data related to the Virtual Machines that support Solution components is encrypted at rest, replicated in multiple local copies and Geo-redundant.

02 / Instance layer

Using the cloud platform's native capabilities, ToolsGroup performs a full backup of each compute node or virtual machine, retained for 15 days on a rolling basis. These backups are stored in multiple copies, Geo-redundant and encrypted at rest.

03 / Application data layer

This includes Customer Data stored inside the Solution and is backed up daily and kept for 15 days rolling.

Security Incident Management

ToolsGroup maintains policies and procedures to detect, manage and track any security incidents or events. The primary aim is the prompt detection of any incident or potential incident to reduce the risk of information exposure and to promptly communicate any breaches to all affected Parties and Authorities without undue delay.

To support this process ToolsGroup has implemented:

  • A security incident response plan that clearly defines tasks and activities that need to be carried out to properly evaluate, classify, mitigate and respond to security incidents.
  • The definition of security-related roles and responsibilities within the organization, including the role of Information Security Manager and an oversight committee.
  • Processes aimed at the continuous improvement of security-related aspects in the Organization that include the periodic review of existing measures and their effectiveness.

Compliance

Compliance plays a critical role in providing assurance for Customers and in securing and bolstering the trust between the Customer and ToolsGroup. ToolsGroup maintains compliance with both local regulations as well as International Standards widely recognized in the industry.

/ ISO/IEC 27001:2022

ISO/IEC 27001 is a security standard that formally specifies an Information Security Management System (ISMS) that is intended to bring information security under explicit management control. As a formal specification, it mandates requirements that define how to implement, monitor, maintain and continually improve the ISMS. It also prescribes a set of best practices that include documentation requirements, divisions of responsibility, availability, access control, security, auditing, and corrective and preventive measures.

ToolsGroup currently maintains an active Certification in good standing for ISO/IEC 27001:2022. The Certificate as well as the Statement of Applicability can be shared with Prospects and Customers for review upon request. The scope of the certification is “The Information Security Management System for the provisioning of SaaS (Software as a Service) services for Planning and Business Analytics solutions”.

As part of this process ToolsGroup has developed an Information Security Management System (ISMS) that is distributed to employees and contains policies, procedures, modules and instructions for internal use.

GDPR and Data Protection

ToolsGroup B.V. is headquartered in Amsterdam and operates under the EU General Data Protection Regulation (GDPR). When our SaaS solutions process personal data on behalf of customers, ToolsGroup acts as a data processor. We process that data only on the customer's documented instructions and under a Data Processing Agreement.

  • Data residency: The customer specifies the geography, and ToolsGroup deploys the solution in a region that meets its data-residency requirements.
  • International transfers: Personal data is transferred outside the EEA only with appropriate safeguards, such as the EU Standard Contractual Clauses (2021/914) or an adequacy decision.
  • Sub-processors: We engage a limited number of sub-processors, bound by data protection obligations equivalent to our own. The current list is available on request, and customers receive advance notice of changes.
  • Security of processing: The technical and organizational measures described on this page are part of our ISO/IEC 27001:2022-certified Information Security Management System.
  • Breach notification: We notify affected customers without undue delay after becoming aware of a personal data breach.
  • Data subject rights: We help customers respond to data subject requests, such as access, correction and deletion.

ToolsGroup has appointed an external Data Protection Officer. For details on how we handle personal data, see our Privacy Policy and our Transparency Document, which covers GDPR Articles 13 and 14 and CCPA/CPRA. Our standard data protection terms are described in the General Terms and Conditions for Data Protection.

Contact Our Security Team

Have a question about how we protect your data, or need documentation for your vendor assessment? Our Information Security team is here to help.

Contact us at security@toolsgroup.com to:

  • Request our ISO/IEC 27001:2022 certificate and Statement of Applicability
  • Request our penetration test summary (under NDA)
  • Discuss security questionnaires or due-diligence requirements
  • Report a suspected security vulnerability or incident

Trust & Transparency Center